.com 
persistentnetwork.com
PersistentNetwork.com combines a powerful infrastructure concept with one of technology’s foundational words. “Persistent” suggest…
ai
View listing
Home / Domains / runtimethreat.com
An attack rarely reveals its full intent in a single event. Suspicious execution can unfold through process activity, unexpected network connections, privilege changes, and attempts to acces
One message opens the conversation — availability, price, and how the transfer works.
Inquire on WhatsAppPrivate conversation. No account, no public bidding.
Prefer a form? Send a message
About this name
KNOW THE THREAT BEHIND THE EXECUTION.
An attack rarely reveals its full intent in a single event. Suspicious execution can unfold through process activity, unexpected network connections, privilege changes, and attempts to access sensitive resources. RuntimeThreat.com suggests a security intelligence brand for connecting those clues into attack behavior narratives and investigable execution paths.
A runtime threat intelligence platform could organize execution signals, correlate suspicious behaviors, map possible attack sequences, and provide investigation context for security teams. RuntimeThreat evokes a focused research and analysis layer: identify the behavior, connect the evidence, and clarify what warrants attention.
Classify suspicious actions and execution patterns.
Correlate events into possible multi-stage attack paths.
Connect process, file, identity, and network signals.
Present findings for triage and incident review.
RuntimeThreat.com could anchor a runtime threat intelligence platform, behavioral attack analysis product, cloud workload investigation service, execution-based threat hunting toolkit, process anomaly research console, exploit behavior knowledge base, container threat analysis engine, incident investigation dashboard, or AI-assisted security research platform. Its positioning emphasizes understanding the threat rather than merely promising to block it—connecting suspicious actions with technical evidence.
A natural positioning for runtime threat hunting, cloud workload investigation, process behavior analysis, and security operations research.
An alternative direction for attack-path visualization, exploit behavior research, threat case management, and incident reconstruction tools.
Also available
PersistentNetwork.com combines a powerful infrastructure concept with one of technology’s foundational words. “Persistent” suggest…
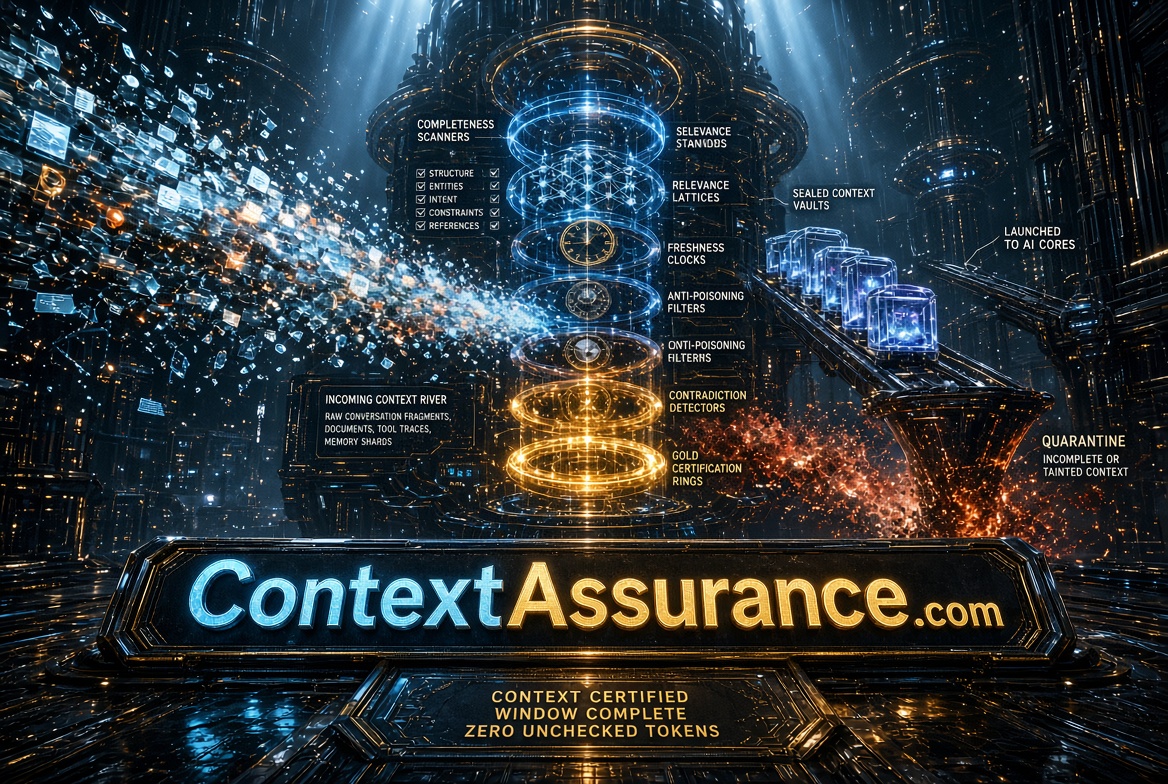
ContextAssurance.com is a precision AI infrastructure name for checking whether the information supplied to a model or agent is ap…

A highly descriptive .COM for quantitative modeling, computational research, forecasting, financial simulation, risk analysis, art…